The Vault Launches Its own MPC Library for Institutional Custody
Barcelona, 17 September 2026. The Vault, the institutional digital asset custody platform regulated in Switzerland and the EU, has launched its own multi-party computation (MPC) library, the cryptography that allows separate parties to hold shares of a signing key so that a complete private key never exists on any device or server. The launch follows an independent security audit by blockchain security firm Halborn, which issued its final report earlier this week confirming that all findings raised have been remediated and verified.
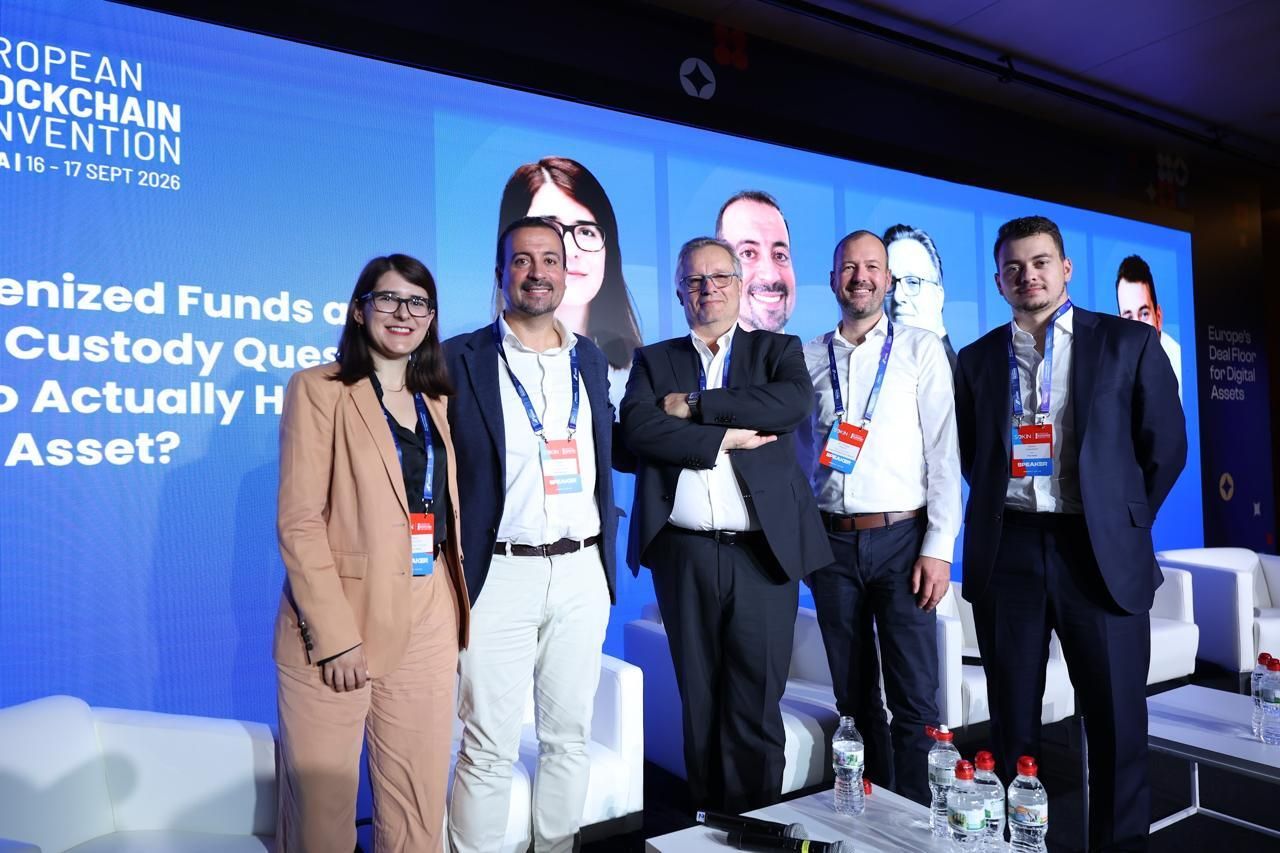
Artem Stopnevich, chief executive of The Vault, presented it at the European Blockchain Convention in Barcelona, describing it as the first sovereign cryptographic library for institutional custody in Europe, following the completion of an independent audit by Halborn.
The library enforces The Vault’s co-signing model, under which no single party, including The Vault itself, can authorize a transfer on its own. Most custody providers license this component from an external vendor, a decision that ties them to the vendor’s release cycle for security fixes, to the curves and protocols it supports, and to the level of disclosure it permits during due diligence.
The Vault builds it in-house, which is what the company means by sovereign cryptography: the code, the signing protocol, and the release schedule sit with the platform, so fixes ship on The Vault’s own timetable, auditors see the whole codebase, and the protocol can move forward as standards evolve.

“For an institution, custody is a risk decision that has to be signed off internally, and it comes down to a single question: who is able to move an asset, and under what controls,” said Artem Stopnevich, Chief Executive Officer of The Vault, speaking on the sidelines of the European Blockchain Convention in Barcelona, where he joined a panel on the custody of tokenised funds. “We are the only EU-regulated custody provider running institutional MPC cryptography of its own making, and we took the view that we would not put it in front of clients until somebody outside this company had taken it apart at the protocol level, which is what Halborn has now done.”
The library implements distributed key generation, resharing, refresh and recovery, and threshold ECDSA and EdDSA signing, together with commitment, oblivious transfer and zero-knowledge proof primitives, and the transport that carries protocol messages between signers. It is written in Rust, a systems language whose compiler enforces memory safety without a garbage collector, and the same implementation runs on The Vault’s servers and inside the mobile signer on iOS and Android, so the audit covers a single codebase.
“The properties we need at the signing layer are the ones the compiler can enforce for us: no use-after-free, no data races across the concurrent rounds of a protocol, and explicit control over how key material is held in memory and erased once it is no longer needed,” said Yurii Derbasov, Chief Technology Officer at The Vault. “The language does not make a protocol correct, which is why the design itself needed an external review of this depth.”
Halborn’s engagement covered 91 files across the cryptographic core, its test suite and the iOS and Android signer applications. Findings raised during the review were addressed in the codebase as the engagement progressed, and Halborn verified each remediation against the commit that implemented it, confirming the final items in August 2026.
“It was a pleasure to work together with The Vault on securing their MPC custody. Security was clearly a priority for their team, and all findings raised during the engagement were remediated and verified. For institutional custody, proprietary cryptography gives providers direct control over security fixes and protocol updates, and allows auditors to examine the complete implementation rather than stopping at a vendor boundary. That matters when clients are performing technical due diligence on who can move their assets.” said Gabi Urrutia, SVP Security & Field CISO at Halborn.
In the co-signing model, the client holds a key share on their own device, and the mobile signer is the application through which that share is held and used. It is available as an add-on to The Vault’s SaaS custody product.
Looking ahead, The Vault intends to publish the Rust library as open source, so that the cryptography can be examined by anyone, and its cryptography team is working on two new protocols.
The first is a threshold variant of ML-DSA, the post-quantum signature scheme that NIST standardized under FIPS 204 for a single signer; threshold signatures have no NIST-standardised form today, and candidate constructions, classical and post-quantum alike, are going through competitive selection under the NIST First Call for Multi-Party Threshold Schemes, which opened in January 2026. The second is a new threshold post-quantum password-authenticated key exchange, or PAKE.
The full report is available to institutional clients on request (media@thevault.inc).
About The Vault
The Vault is a Swiss and EU-regulated institutional infrastructure platform for digital assets, serving corporate treasuries, financial institutions, family offices, and payment providers. It covers the full lifecycle, from secure custody and treasury operations to back-office management and wallet infrastructure, and is built on proprietary threshold MPC cryptography developed by an in-house research team. It is available in SaaS and On-Premise, with a bespoke modular architecture that can be customized to each company’s needs and frameworks.
The post The Vault Launches Its own MPC Library for Institutional Custody appeared first on BeInCrypto.
Read moreLatest News